

Ready to build better conversations?
Simple to set up. Easy to use. Powerful integrations.
Get free accessReady to build better conversations?
Simple to set up. Easy to use. Powerful integrations.
Get free accessMost security teams know this problem well. It is manual, repetitive, and relentless. Analysts jump between 30 tools to review alerts, chase context, run investigations, and build new detections. A single investigation can take 30 minutes, and the alerts never stop arriving.
At Aircall, our team faced more than 300 alerts a month. We wanted the depth of a large enterprise security program without the headcount that usually comes with one. So we built our own AI triage bot. It now triages those 300 alerts and leaves about 10 investigations a week for our engineers to dig into.
Here’s how we did it…
The problem: security operations don't scale just by adding people
Alert volume grows with your product, your customers, and your attack surface. Human review doesn’t grow at the same pace. Teams in our position have three options, and none of them are ideal.
Expand headcount. Hiring more analysts is slow and expensive, and skilled security engineers are hard to find.
Outsource to a managed detection and response provider. This adds cost and distance, and it can dilute the context that makes triage accurate.
Compromise on security. Review fewer alerts, accept more risk, and hope the gaps don't matter. But they always do.
We refused to review fewer alerts. That meant changing the work, not the size of the team.
The shift: from a large operations force to a focused engineering team
For years, strong security meant a large security operations force, a separate security engineering function, and a dedicated incident response team. That structure works, but it's costly and it can bury expensive talent in repetitive triage.
Our AI triage bot changed the model. Instead of a large team clearing a queue, we now run a small team of skilled engineers who get called in only when something looks genuinely concerning. The rest of the time, those engineers do the work that strengthens our foundations: hardening systems, improving logging, and developing new detections. That kind of depth used to take a much larger program. A lean team can build it now.
How the AI triage bot works
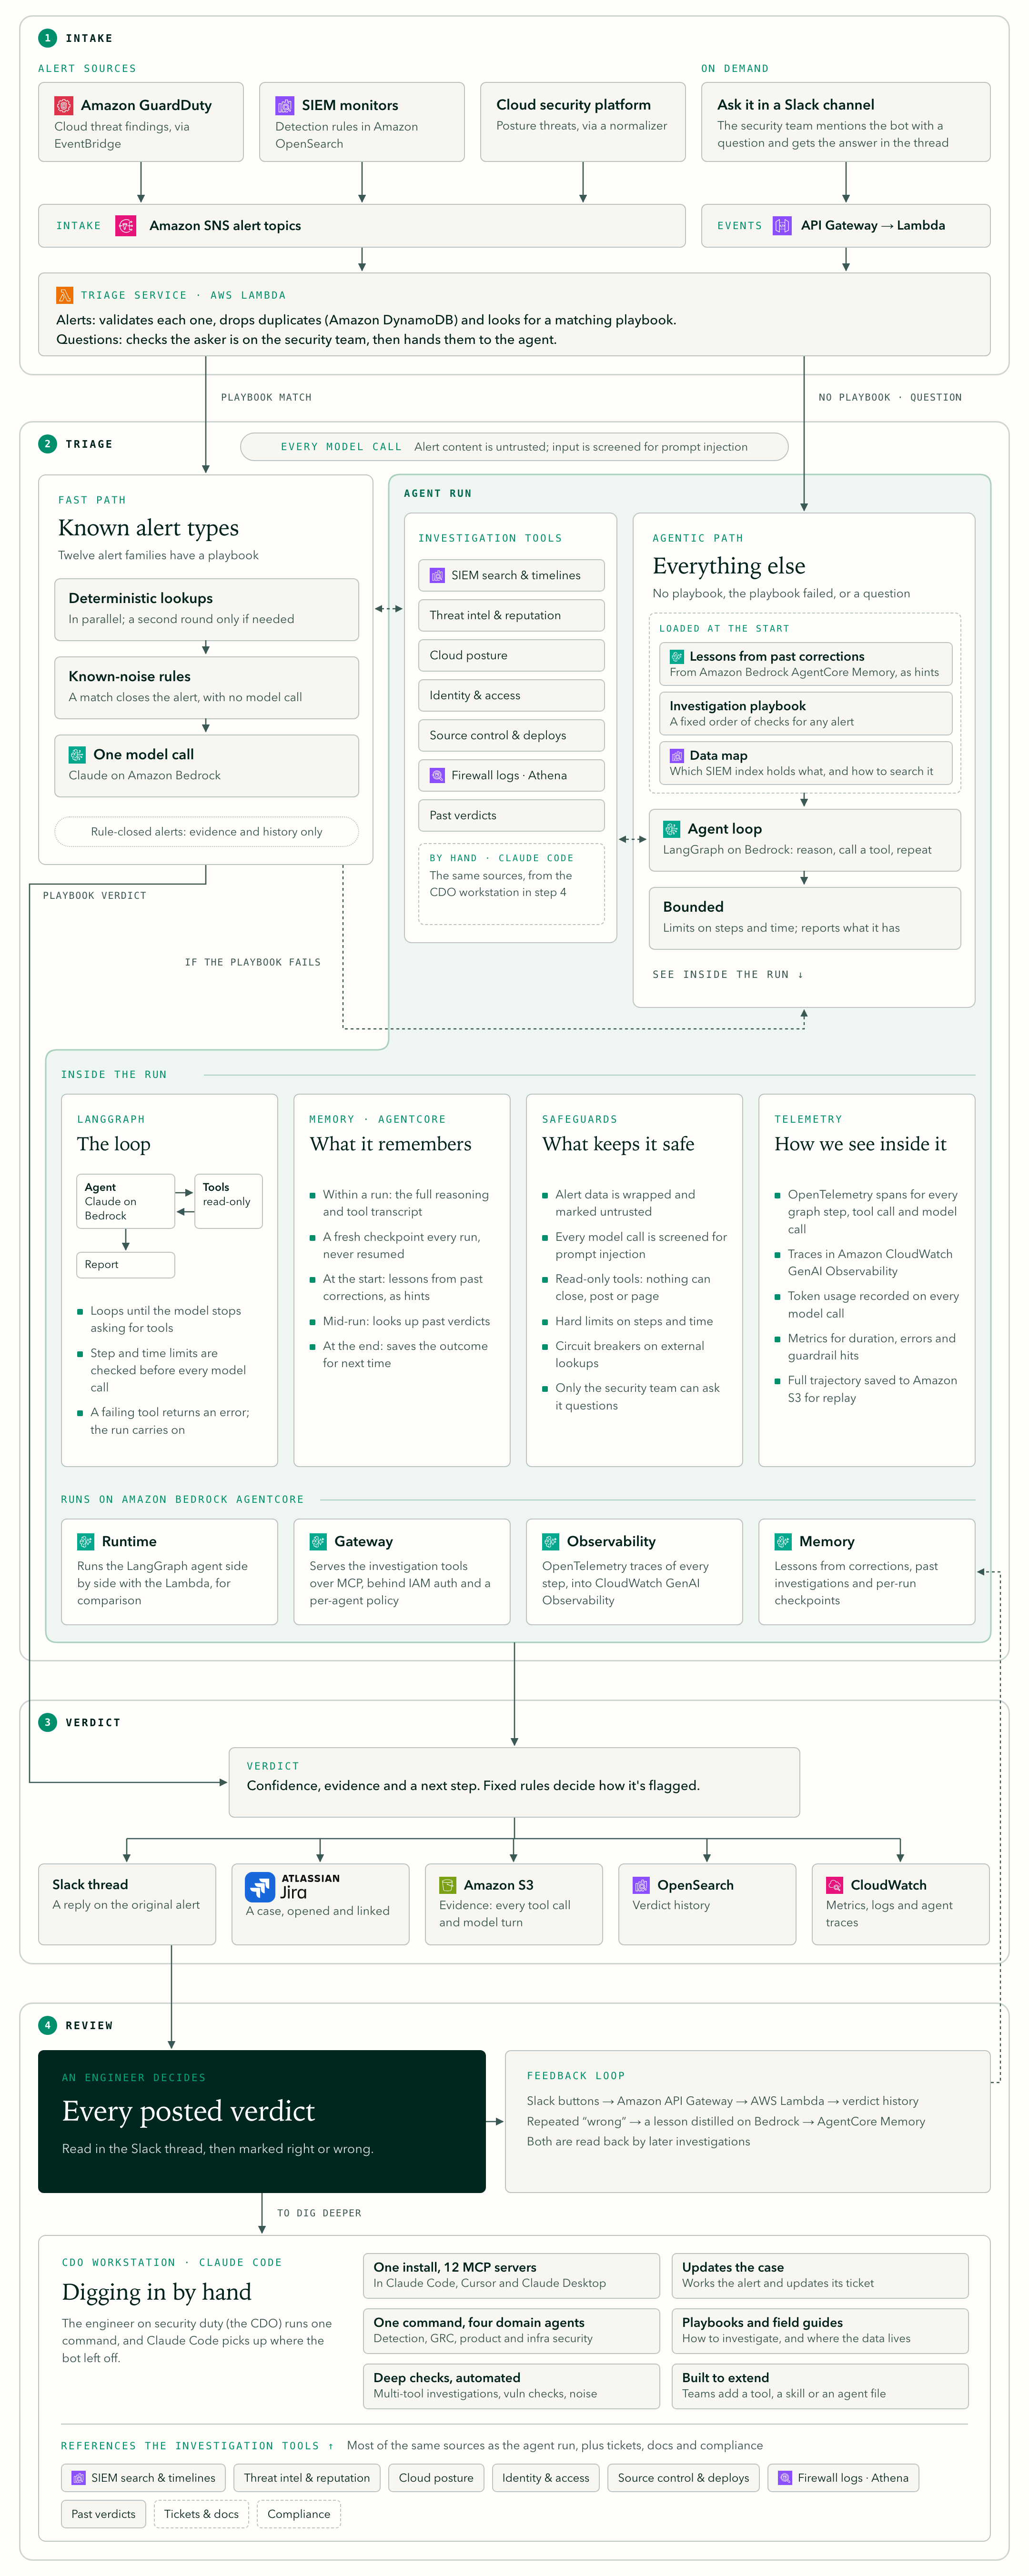
The bot sits at the front of our alert pipeline and does the first pass that used to consume our analysts' days.
It ingests every alert. All 300 or more a month flow into one place instead of 30 scattered tools.
It gathers context automatically. The bot pulls the context a human would normally collect manually, so nothing waits on someone switching between dashboards.
It assesses and prioritizes. Each alert gets triaged against what we know about normal behavior. Clear noise gets closed. Real risk gets surfaced.
It escalates the few that matter. Roughly 10 investigations a week reach a human, with the context already attached.
The bot does the first pass. Engineers still decide what matters.
The benefits of our AI triage bot
Less manual review. More than 300 alerts still arrive each month. About 10 a week need a person.
Faster response. Context arrives with the alert, so engineers can start investigating instead of spending time gathering context.
Deeper security work. Freed from the queue, our engineers build hardening, logging, and detections that used to be out of reach.
A leaner, sharper team. We get enterprise-grade coverage without an enterprise-sized operations force.
Why we built it ourselves
We could have bought a tool, but we built our own for three reasons.
Context. Our team knows our environment better than any outside product does. That knowledge makes triage more accurate.
Control. Building it ourselves means we decide what the bot sees, how it handles data, and where the guardrails sit.
Compounding value. Every detection we add and every rule we tune makes the bot smarter for us specifically, not for a vendor's average customer.
How your team can move toward this
You don't need to rebuild your whole program to start. Focus on moving the manual work away from your best people.
Map your alert sources. Count how many tools your analysts touch and how long a typical investigation takes. That's your baseline.
Find the repetitive triage. Identify the alerts that follow a predictable pattern. Those are the first candidates for automation.
Automate context gathering first. Before you automate decisions, automate the collection of signals a human needs to decide.
Escalate, don't replace. Let the system close clear noise and route the rest to humans with context attached.
Reinvest the time. Point your engineers at hardening, logging, and detection development. That's where a lean team builds enterprise depth.
Start small, measure the drop in manual review, and expand from there. The goal is a team that spends its time where it counts.
Security operations don't have to mean a wall of alerts and a growing headcount. With the right automation, a small team can protect a fast-growing business with the rigor of a much larger one. That's the model we run at Aircall, and it's the model we think more teams should build.
To learn more about how we protect our customers and their data, explore Aircall's approach to security and compliance.
Published on October 5, 2026.
